Cloud security assessment
Know which risks matter.
A customer asks how secure your platform is. You need evidence, not a checklist.
You leave with
See the scope An evidence-backed risk register, prioritized fixes and a leadership readout.
Cloud & software engineering
Build the next thing. Fix what’s holding you back. Senior engineers, cloud expertise and software that runs on your terms.
Your cloud. Your code. Your team, stronger.
Built for the stack
you already run.
A critical release. A platform under pressure. A security review on the calendar. Start with the problem; we’ll agree the right way forward.
Senior platform, backend and security engineers in your repositories, your planning and your reviews. Accountable to your engineering lead.
 Explore embedded engineers
Security and architecture reviews with evidence, priorities and a plan your team can act on.
Explore cloud advisoryWallets, API controls, video calls and Kubernetes tools. Built by us. Run where you choose.
Meet the productsFind your next step
Defined questions. A fixed scope and fee. Findings your engineers can use.
Read a sample findingCloud security assessment
A customer asks how secure your platform is. You need evidence, not a checklist.
An evidence-backed risk register, prioritized fixes and a leadership readout.
Cloud architecture review
Your platform is growing. Reliability, cost or complexity is getting in the way.
An architecture gap analysis, recovery review and sequenced improvement plan.
Security remediation
You know what needs fixing. Your engineers are already committed to the roadmap.
Reviewed code and configuration changes, validation evidence and a handover.
Fixed-scope reviews · Monthly engineering engagements · Commercial product licences
 Your environment.
From an auditable wallet ledger to a Kubernetes workbench. Choose a product and explore how it fits your stack.
Wallet infrastructure for business, on a ledger you can audit.
Explore WalletDAPI keys, quotas and cluster-wide rate limits for KrakenD Community Edition.
Explore TollgateReal-time audio and video calls, running where you choose.
Explore TeleA self-hosted Kubernetes dashboard with a read-only AI SRE.
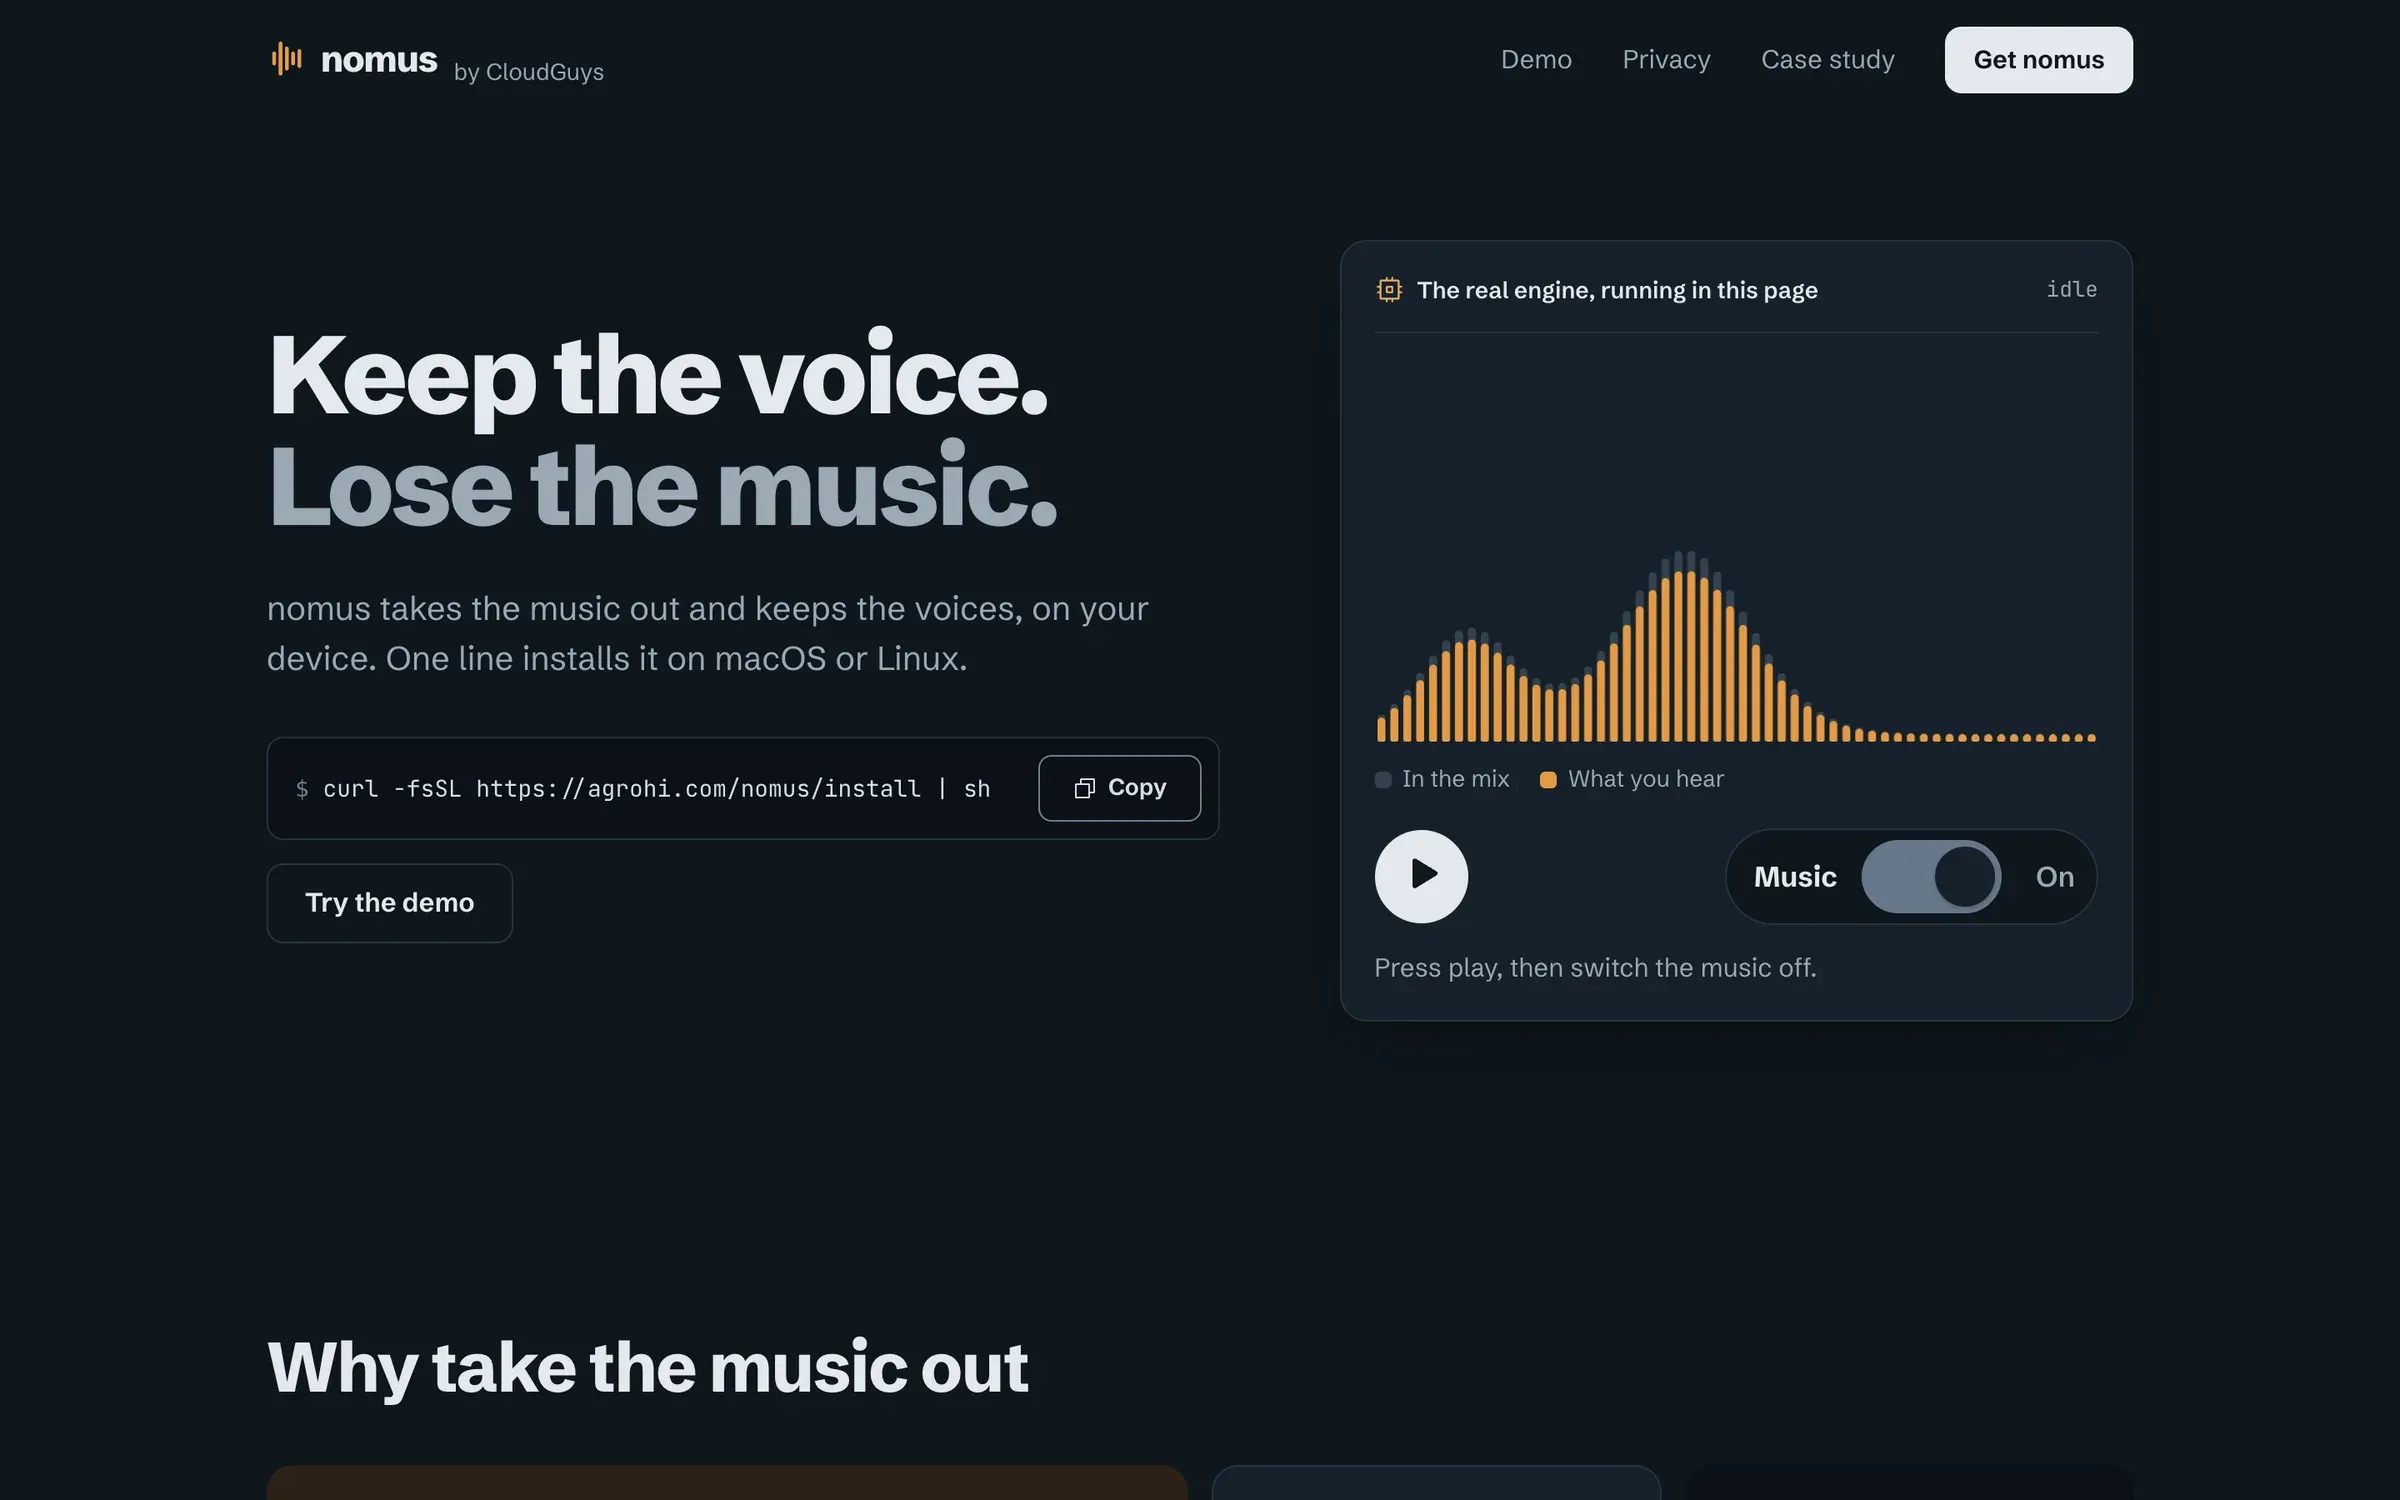
Explore BerthKeep the voice, lose the music, on your own device.
Explore nomusThe way we work
Work that moves you forward. Knowledge that stays with your team. Ownership that stays with you.
We define the systems, deliverables, fee and timeline before the work starts.
Your accounts, repositories and change process. Scoped read-only access first; production changes agreed explicitly.
Reviewed changes, decisions and runbooks in your repositories. A handover your team can use.
Have a different question?
[email protected]
We agree the role first: outcomes, systems, access and the hours that overlap with your team. The engineer then works in your repositories, chat and planning under your engineering lead. Progress is reviewed monthly, and the work is documented and handed over when the engagement ends.
Yes. WalletD, Tollgate, Tele and Berth deploy in your own cloud, cluster or private network, and nomus runs on the user's device. Deployment, integrations and data residency are agreed with you before launch.
We agree a scope across identity and access, network exposure, data protection, logging, cloud configuration, and delivery controls. Findings include evidence, impact, remediation guidance, and review limitations.
We start with documentation and scoped read-only access where practical. Privileged access, production changes, evidence handling, and retention are agreed explicitly before work begins.
Yes. Remediation can be a separate engagement or part of the agreed scope. We work in your accounts and repositories, document changes, and validate the controls after implementation.
A configuration and architecture assessment does not itself provide a penetration test or certification. Any testing or compliance evidence support is defined separately; formal certification requires the appropriate independent assessor.
We support organizations using AWS, Google Cloud, Azure, Kubernetes, and infrastructure as code. Engagements are shaped around your systems, risk priorities, internal team, and operational constraints.
We scope the work before quoting. Account count, workload complexity, access arrangements, and required deliverables determine the fee and timeline. A discovery conversation establishes these details without promising a complete free audit.
Let’s make the next step clear
Tell us what you’re building, what’s getting in the way and when it matters. We’ll reply within one business day with a proposed first step.
[email protected]